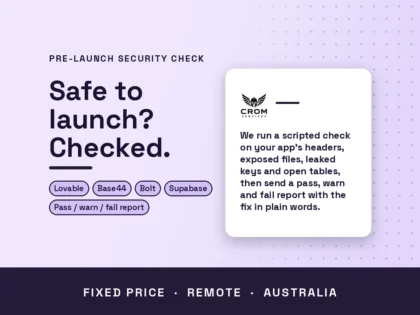
In 1 to 3 days: a scripted pre-launch security check on your Lovable, Base44, Bolt or Supabase app, with a plain-language pass, warn and fail report. This is a scripted check, not an AI vouching for the app, and not a penetration test or a certification.
I Will run a pre-launch security check on your Lovable, Base44, Bolt or Supabase app, with a pass or fail report
Scripted pre-launch security check with a pass, warn and fail report.
- Scripted check of headers, HTTPS, exposed files, CORS, secrets in the client JavaScript, Supabase tables (if present) and a gentle 20-request rate-limit test
- Markdown and HTML report with pass, warn and fail, evidence, and the fix in plain words
- Secret values are never written in the report
Everything in Quick scan, plus a plain-language fix list in order.
- Everything in Quick scan
- Plain-language fix list, in order, written for a Lovable, Base44, Bolt or Supabase project (what to change, and where)
- Short note on anything that looks like a platform default (for example a missing header on an app domain) so you know what you can fix yourself
Everything in Scan + fix list, plus we apply the safe fixes and re-run the script.
- Everything in Scan + fix list
- We apply the safe fixes we can: security headers, removing exposed files and source maps, tightening Row Level Security, and taking leaked secret keys out of the client
- We run the script again and send the before and after reports
- Key rotation in Stripe, Supabase or other providers is guided; you approve any rotate or revoke step first. Bigger rebuilds or a full source-code review are quoted separately
Request a Custom Offer
Log In to Request a Custom Offer
Create a free account or log in to request a personalised offer from this Zinner.
Log In / RegisterAsk a Pre-Sale Question
Log In to Ask a Question
To reduce platform spam, pre-sale messages can only be sent by logged-in users.
Create a free account or log in to message this Zinner directly.
Log In / RegisterAt a Glance
Key details about this service to help you decide. Generated by Zinn Hub, not the seller.
Value Position
Check Method
Platforms Covered
What Gets Checked
Delivery Format
What You'll Receive
Full Description
Ready in 1 to 3 days, depending on the package. A Lovable, Base44, Bolt or Supabase app can look finished and still ship with missing security headers, a public .env file, a secret key in the JavaScript, or a database table that anyone can read. Most owners never see this, because the app looks fine in the browser.
Crom Services runs a fixed script against your live or staging URL and gives you a clear pass, warn and fail report, with evidence and the fix in plain words. The proof is the script, not an AI writing an opinion.
What you get:
- A scripted check of security headers (CSP, HSTS, X-Frame-Options, X-Content-Type-Options, Referrer-Policy, Permissions-Policy) and the HTTP to HTTPS redirect
- A check for exposed files such as .env, .git and backup files, and for public JavaScript source maps
- A CORS check, and a scan of the public JavaScript for secret keys. The report shows the key type and the first 4 characters only, never the value
- If the app uses Supabase: a read-only list of tables visible to the public anon key, and a flag on any table that returns a row to an anonymous user (LIMIT 1, no writes)
- A gentle rate-limit check: at most 20 requests to one endpoint. Not a load test
- A Markdown and HTML report with pass, warn and fail, evidence, and the fix in plain words
What we need from you:
- The live or staging URL
- If the app uses Supabase and the public key is not already in the page, the project URL and the anon or publishable key only. Never the service_role or secret key
- Which site is in scope, if you have more than one
How it runs: you order and send the URL, we run the script and review the report. On Scan + fix list you also get a plain list of what to change, in order. On Scan + fixes we apply the safe fixes we can, run the script again and send both reports.
Fully remote. No calls needed; questions and handover happen in the order messages.
Fixed price. If it doesn't work as agreed, we fix it free within 7 days of handover. We won't leave you with something broken that we built. The clock starts once we have the URL and any key we need.
Not included, and said plainly: this is a scripted pre-launch check. It is not a penetration test, not a certification, and not a guarantee the app is secure. It does not cover social engineering, paid third-party scanners, or a full source-code review. We quote that work separately so you know the price first.
Zinner Quality Guarantee
Every Zinner is reviewed and approved before joining the platform.
All services are backed by our quality assurance commitment.
Your payment is protected until you approve the delivered work.
Compare Packages
| Feature | Quick scan | Scan + fix list | Scan + fixes |
|---|---|---|---|
| Delivery Time | 1 days | 2 days | 3 days |
| Revisions | 1 | 1 | 1 |
| Scripted check of headers, HTTPS, exposed files, CORS, secrets in the client JavaScript, Supabase tables (if present) and a gentle 20-request rate-limit test | ✓ | ✕ | ✕ |
| Markdown and HTML report with pass, warn and fail, evidence, and the fix in plain words | ✓ | ✕ | ✕ |
| Secret values are never written in the report | ✓ | ✕ | ✕ |
| Everything in Quick scan | ✕ | ✓ | ✕ |
| Plain-language fix list, in order, written for a Lovable, Base44, Bolt or Supabase project (what to change, and where) | ✕ | ✓ | ✕ |
| Short note on anything that looks like a platform default (for example a missing header on an app domain) so you know what you can fix yourself | ✕ | ✓ | ✕ |
| Everything in Scan + fix list | ✕ | ✕ | ✓ |
| We apply the safe fixes we can: security headers, removing exposed files and source maps, tightening Row Level Security, and taking leaked secret keys out of the client | ✕ | ✕ | ✓ |
| We run the script again and send the before and after reports | ✕ | ✕ | ✓ |
| Key rotation in Stripe, Supabase or other providers is guided; you approve any rotate or revoke step first. Bigger rebuilds or a full source-code review are quoted separately | ✕ | ✕ | ✓ |
Service Details
Frequently Asked Questions
No. It is a scripted pre-launch check. It is not a penetration test, not a certification, and not a guarantee the app is secure. Work like that is quoted separately.
No, never. If your app uses Supabase and the public key is not already in the page, we only need the project URL and the anon or publishable key.
On the private job-status page for your order only (a secret URL, not a shared portal). That is where you ask questions, see updates and receive the report.
Quick scan and Scan + fix list only read your public site. On Scan + fixes we apply the safe fixes we can, and you approve any key rotate or revoke step before it happens.
If it doesn't work as agreed, we fix it free within 7 days of handover.
Customer Reviews
See what our customers say about this Zinn