You have an executable or library with no source code and no documentation? I analyze it, reconstruct its logic, and deliver a clear PDF report explaining exactly what it does — entry points, hidden behaviors, protection mechanisms, and risks. You get the answers you need to maintain, audit, or trust the file with confidence.

I Will reverse engineer your binary and deliver a clear PDF analysis report
Fichier jusqu'à 10 MB, analyse statique seule, rapport 10-15 pages
Fichier jusqu'à 50 MB, statique + dynamique en sandbox, rapport 15-25 pages
Toute taille, statique + dynamique + réseau, rapport 25-30+ pages, pseudo-code
Request a Custom Offer
Log In to Request a Custom Offer
Create a free account or log in to request a personalised offer from this Zinner.
Log In / RegisterAsk a Pre-Sale Question
Log In to Ask a Question
To reduce platform spam, pre-sale messages can only be sent by logged-in users.
Create a free account or log in to message this Zinner directly.
Log In / RegisterAt a Glance
Key details about this service to help you decide. Generated by Zinn Hub, not the seller.
Value Position
Analysis Method
Tools Used
Supported Formats
Deliverable
What You'll Receive
Full Description
# Binary Analysis & Reverse Engineering — Clear Report, No Guesswork
You have an executable, a shared library, or a firmware dump with **no source code** and **no documentation**. You need to know what it really does, how it behaves, and whether it is safe to use, ship, or trust.
I analyze your binary and deliver a **clear, structured PDF report** that turns machine code into readable, actionable answers — no jargon, no speculation.
## What you receive
- **A detailed PDF report** (10 to 30 pages depending on complexity)
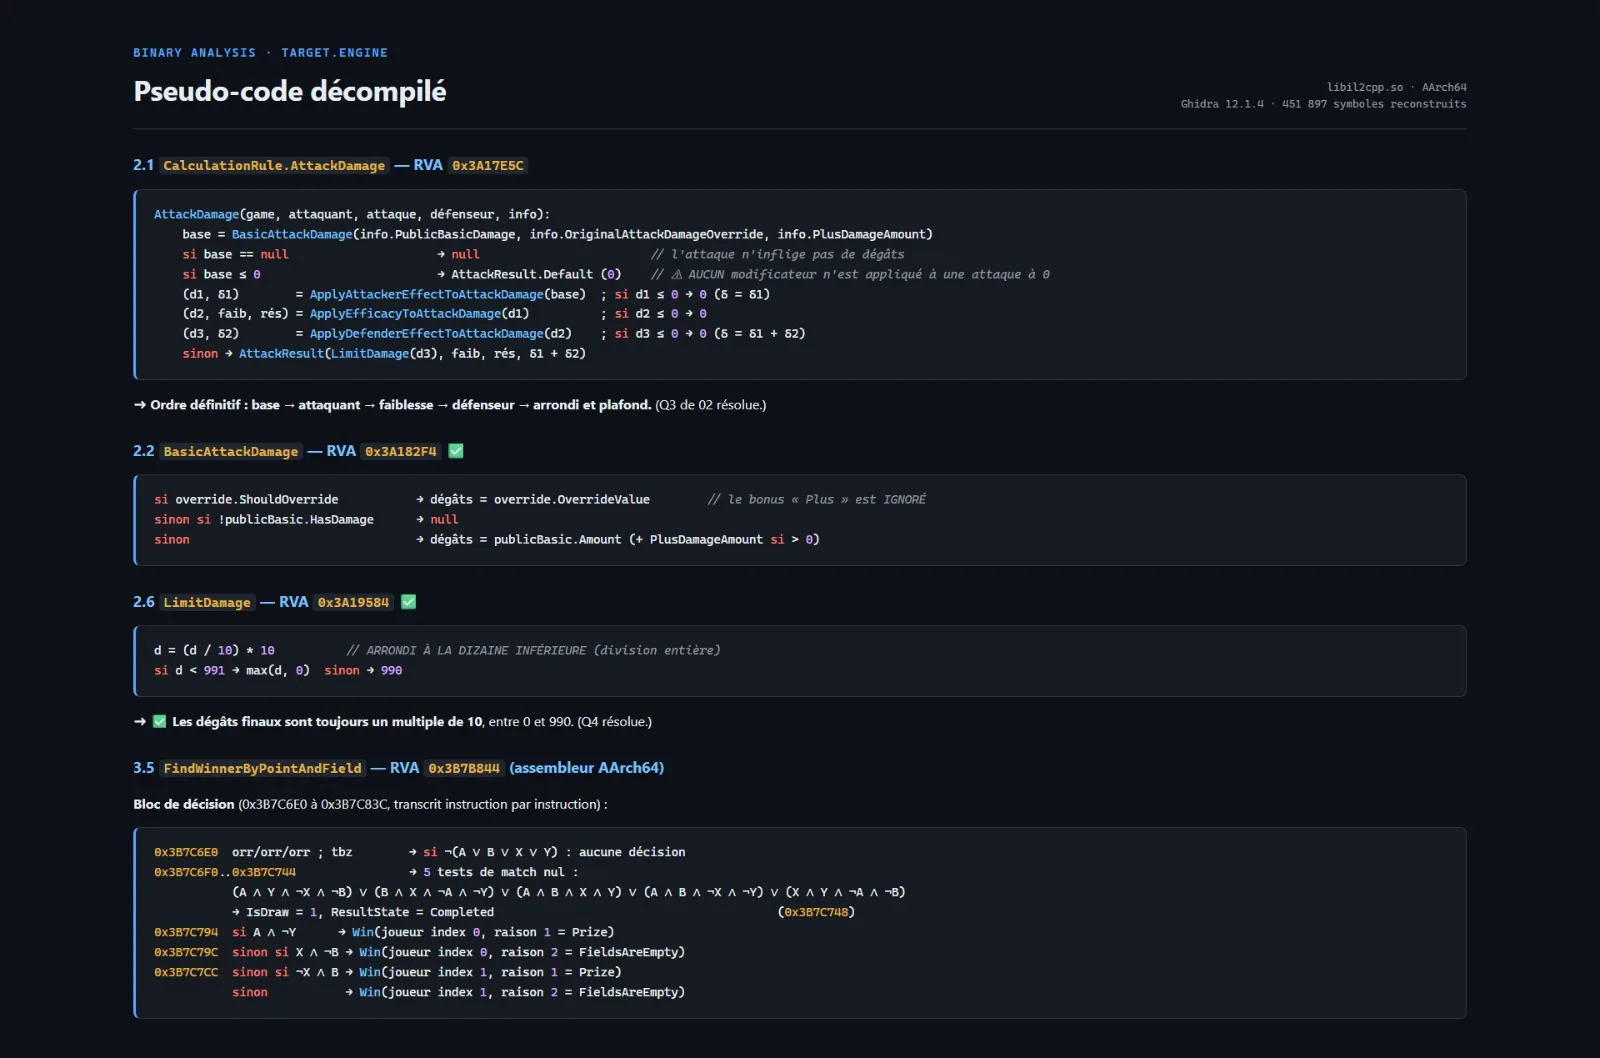
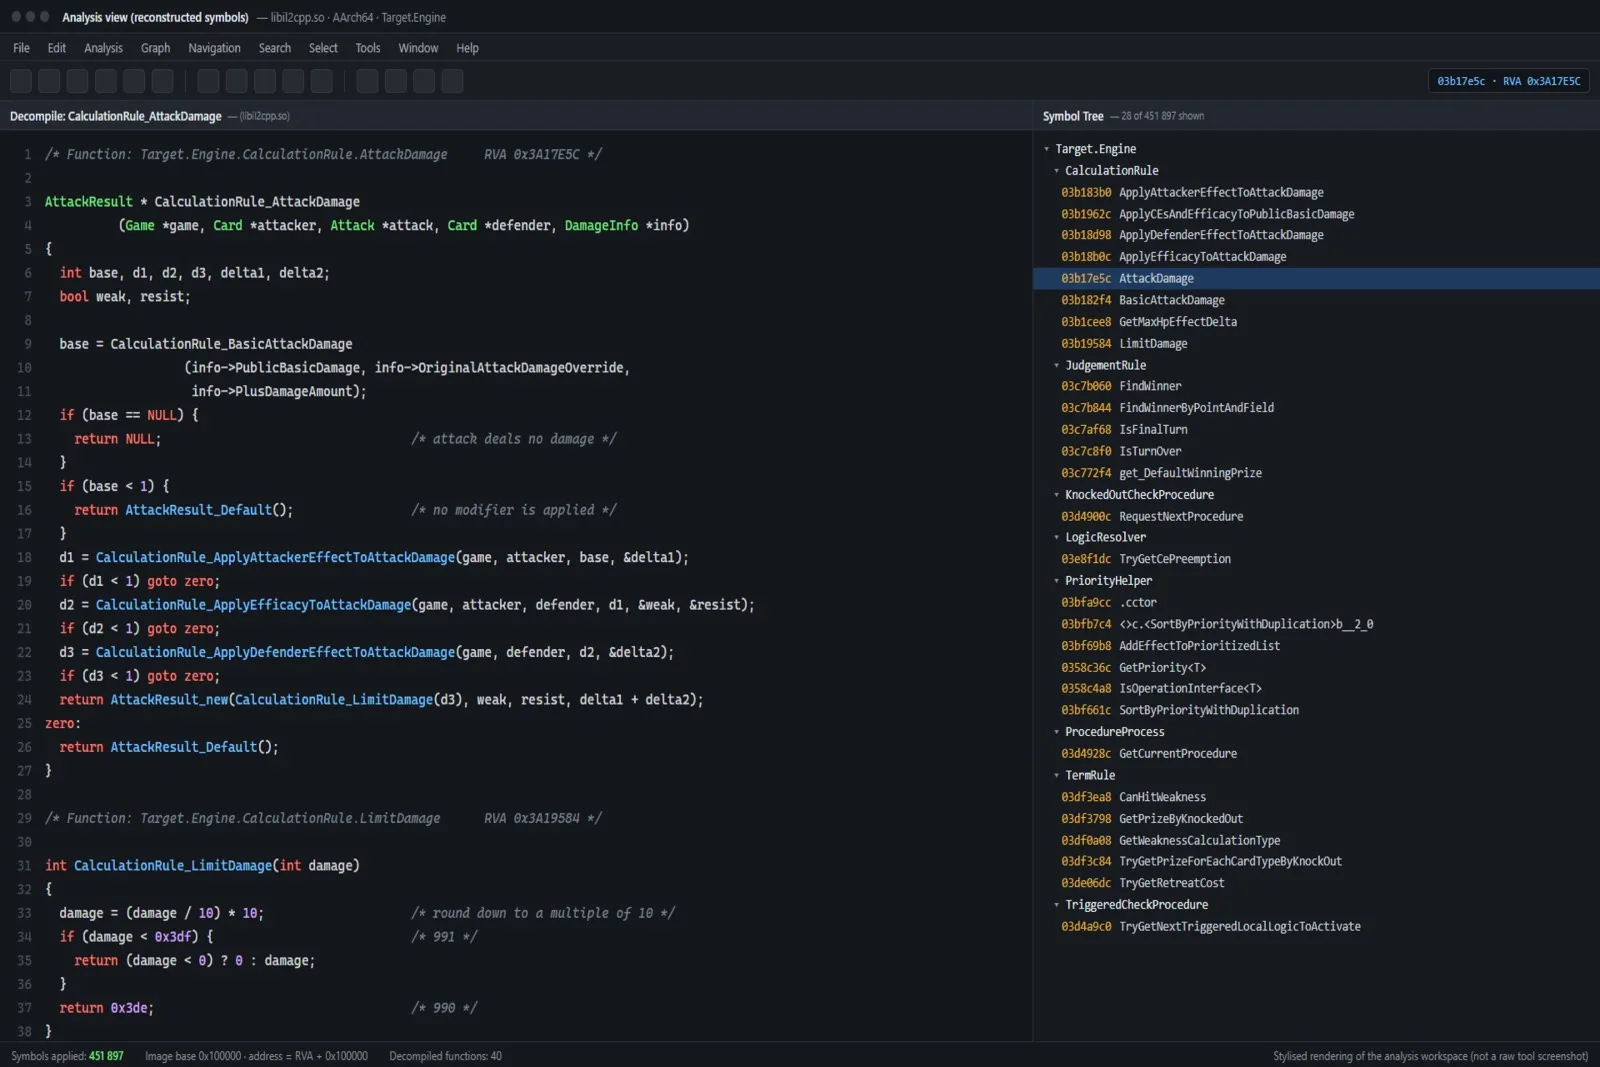
- **Reconstructed logic** in readable pseudo-code (functions, data structures, algorithms)
- **Full behavior map**: entry points, execution flow, network calls, file system access
- **Protection mechanisms** identified: packing, obfuscation, anti-debug, anti-VM, encryption
- **Risk assessment**: suspicious behaviors, hidden features, potential security concerns
- **IOC list** when relevant (IPs, domains, file hashes, registry keys)
- **A 30-minute debrief call** (optional) to walk you through the findings
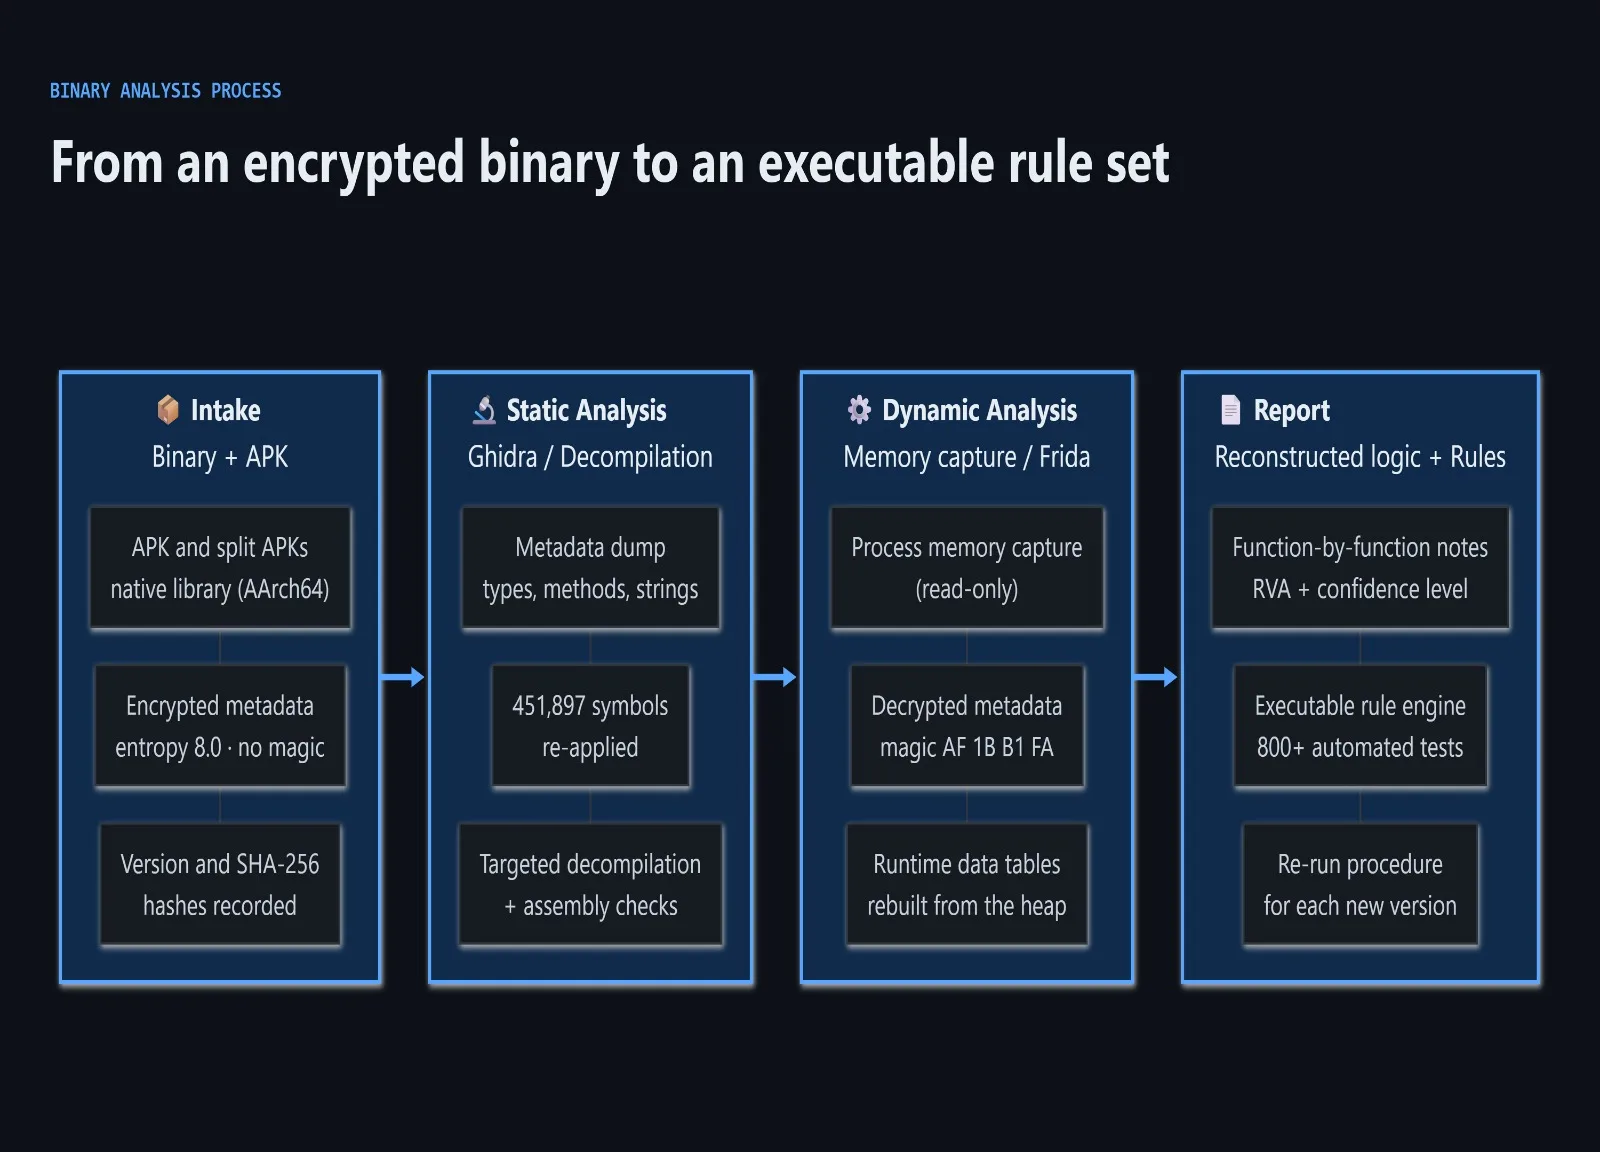
## How it works — 4 steps
1. **Intake (Day 0)** — You send the file and a short description of your goal (audit, recovery, security check, interoperability).
2. **Static analysis (Day 1-2)** — I disassemble the binary, map its structure, identify libraries and protection layers, and reconstruct the main logic.
3. **Dynamic analysis (Day 2-3)** — If needed and safe, I run the file in an isolated sandbox to observe its real behavior (network, files, persistence).
4. **Report delivery (Day 3-5)** — You receive the PDF report, plus a summary email with the 5 key findings. A debrief call can be scheduled if you want to go deeper.
## Packages
### 🔹 Basic — $150
- Files up to 10 MB
- Static analysis only
- 10-15 page PDF report
- Main logic and behavior summary
- Delivery: 3 business days
### 🔸 Standard — $300
- Files up to 50 MB
- Static + dynamic analysis in sandbox
- 15-25 page PDF report
- Full behavior map + IOC list
- Protection mechanisms analysis
- Delivery: 5 business days
### 🔺 Advanced — $500
- Files of any size
- Static + dynamic + network analysis
- 25-30+ page PDF report
- Full pseudo-code reconstruction of key functions
- Network protocol analysis (if applicable)
- 30-minute debrief call included
- Delivery: 7-10 business days
*Custom quote available for obfuscated, packed, or multi-component binaries.*
## What I need from you
- The file to analyze (`.exe`, `.dll`, `.so`, `.bin`, `.elf`, firmware dump, etc.)
- **Confirmation that you own the file or are authorized to analyze it** — I only work on binaries you have the legal right to inspect
- A short note on your goal: security audit, source code recovery, interoperability, incident response, or research
## About me
I am a reverse engineer and software developer with hands-on experience in:
- **Binary analysis**: disassembly with Ghidra and IDA, memory extraction, unpacking, deobfuscation
- **Protocol reconstruction**: decoding proprietary network protocols, encryption schemes, and session logic
- **Logic reconstruction**: rebuilding complete application behavior from binaries, validated by 800+ automated tests
- **Development**: Rust, Python, C/C++, with a focus on performance and reliability
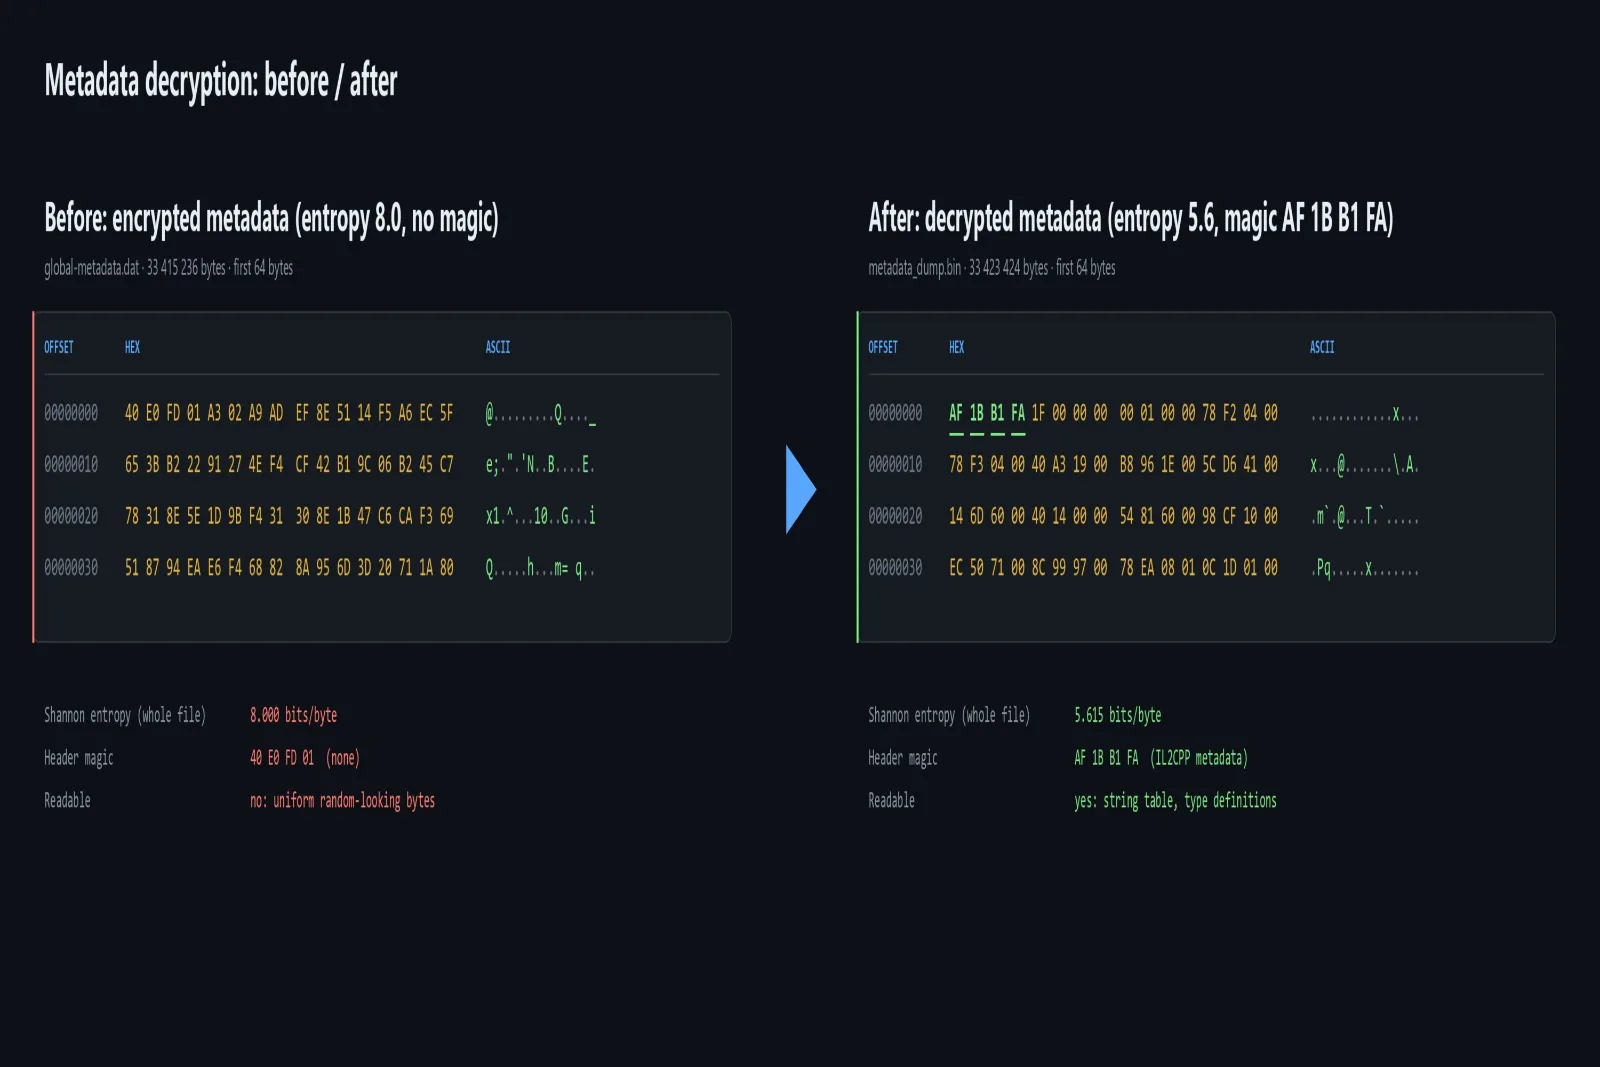
I have reverse engineered a full mobile application end-to-end — from encrypted metadata extraction to a working reconstruction of its business logic, validated against the live service. I bring that same rigor to every file I analyze.
## What makes this different
- **No black box**: every finding in the report is backed by evidence (address, function, or packet)
- **Readable output**: you get pseudo-code and plain-language explanations, not raw disassembly dumps
- **Actionable**: each report ends with concrete recommendations, not just observations
- **Confidential**: files are analyzed in an isolated environment, deleted after delivery, and never shared
## Important notes
- I only analyze files you own or are legally authorized to inspect.
- I do not crack software, bypass licenses, or help circumvent protection for unauthorized use.
- For malware samples, analysis is performed in a fully isolated sandbox — never on a production machine.
- NDA available on request.
---
**Ready to start?** Send me the file and your goal in a message, and I will confirm feasibility and timeline within 24 hours.
Zinner Quality Guarantee
Every Zinner is reviewed and approved before joining the platform.
All services are backed by our quality assurance commitment.
Your payment is protected until you approve the delivered work.
Compare Packages
| Caractéristique | Basic | Standard | Premium |
|---|---|---|---|
| File size limit | Up to 10 MB | Up to 50 MB | Any size |
| Analysis depth | Static only | Static + dynamic (sandbox) | Static + dynamic + network |
| Report length | 10–15 pages | 15–25 pages | 25–30+ pages |
| IOC list | ✕ | ✓ | ✓ |
| Pseudo-code reconstruction | Main logic only | Key functions | Full key functions |
| Delivery time | 3 business days | 5 business days | 7–10 business days |
Portfolio
Examples of the seller's work related to this Zinn.
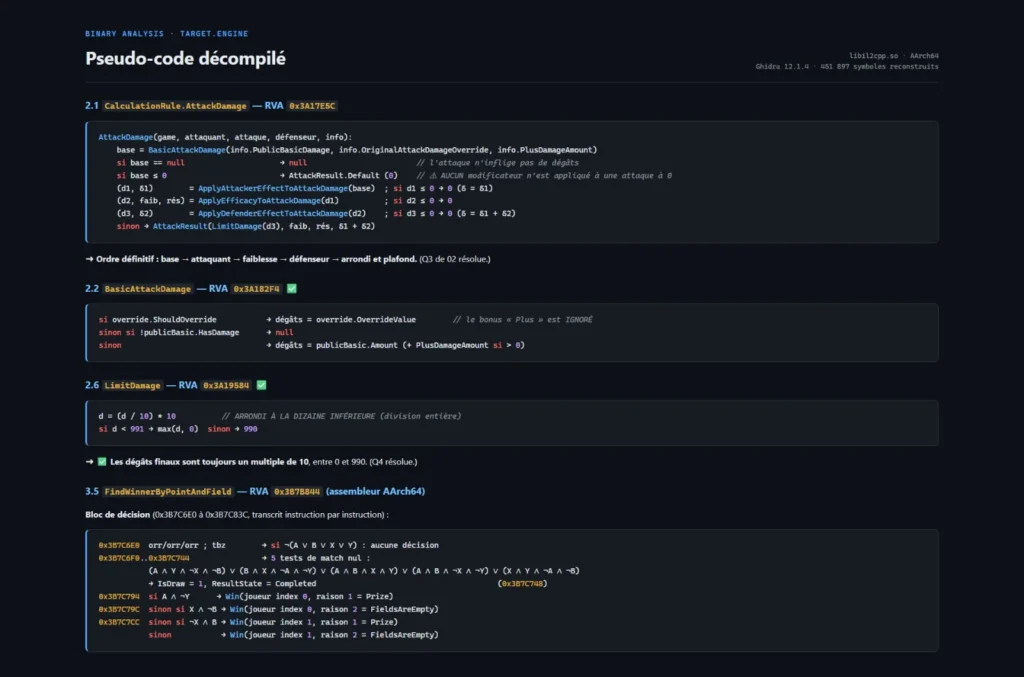
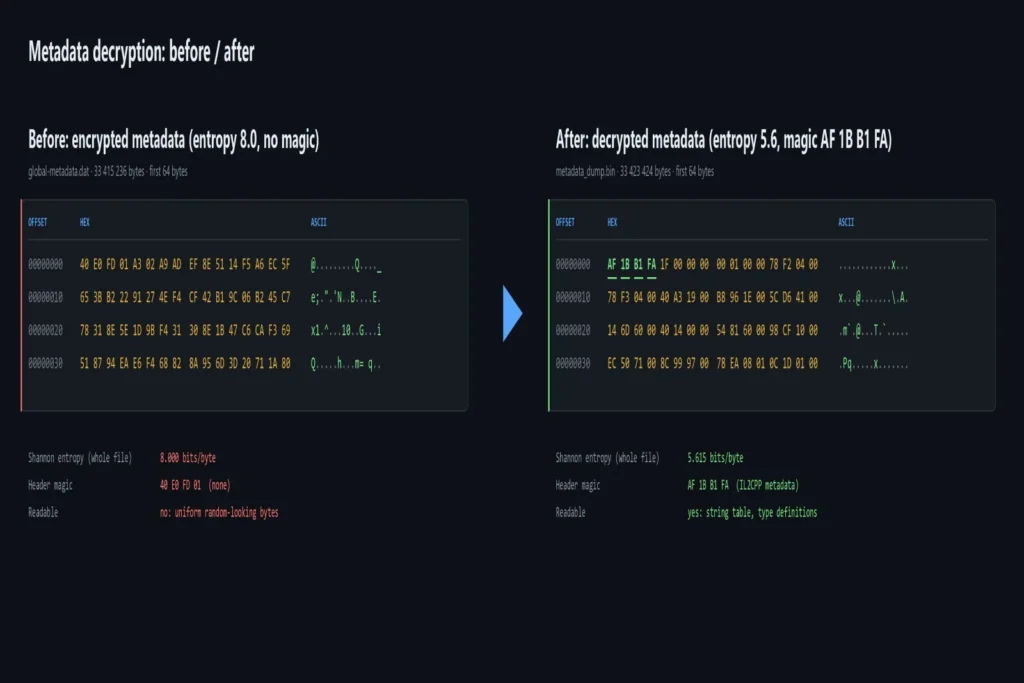
Binary Analysis & Logic Reconstruction
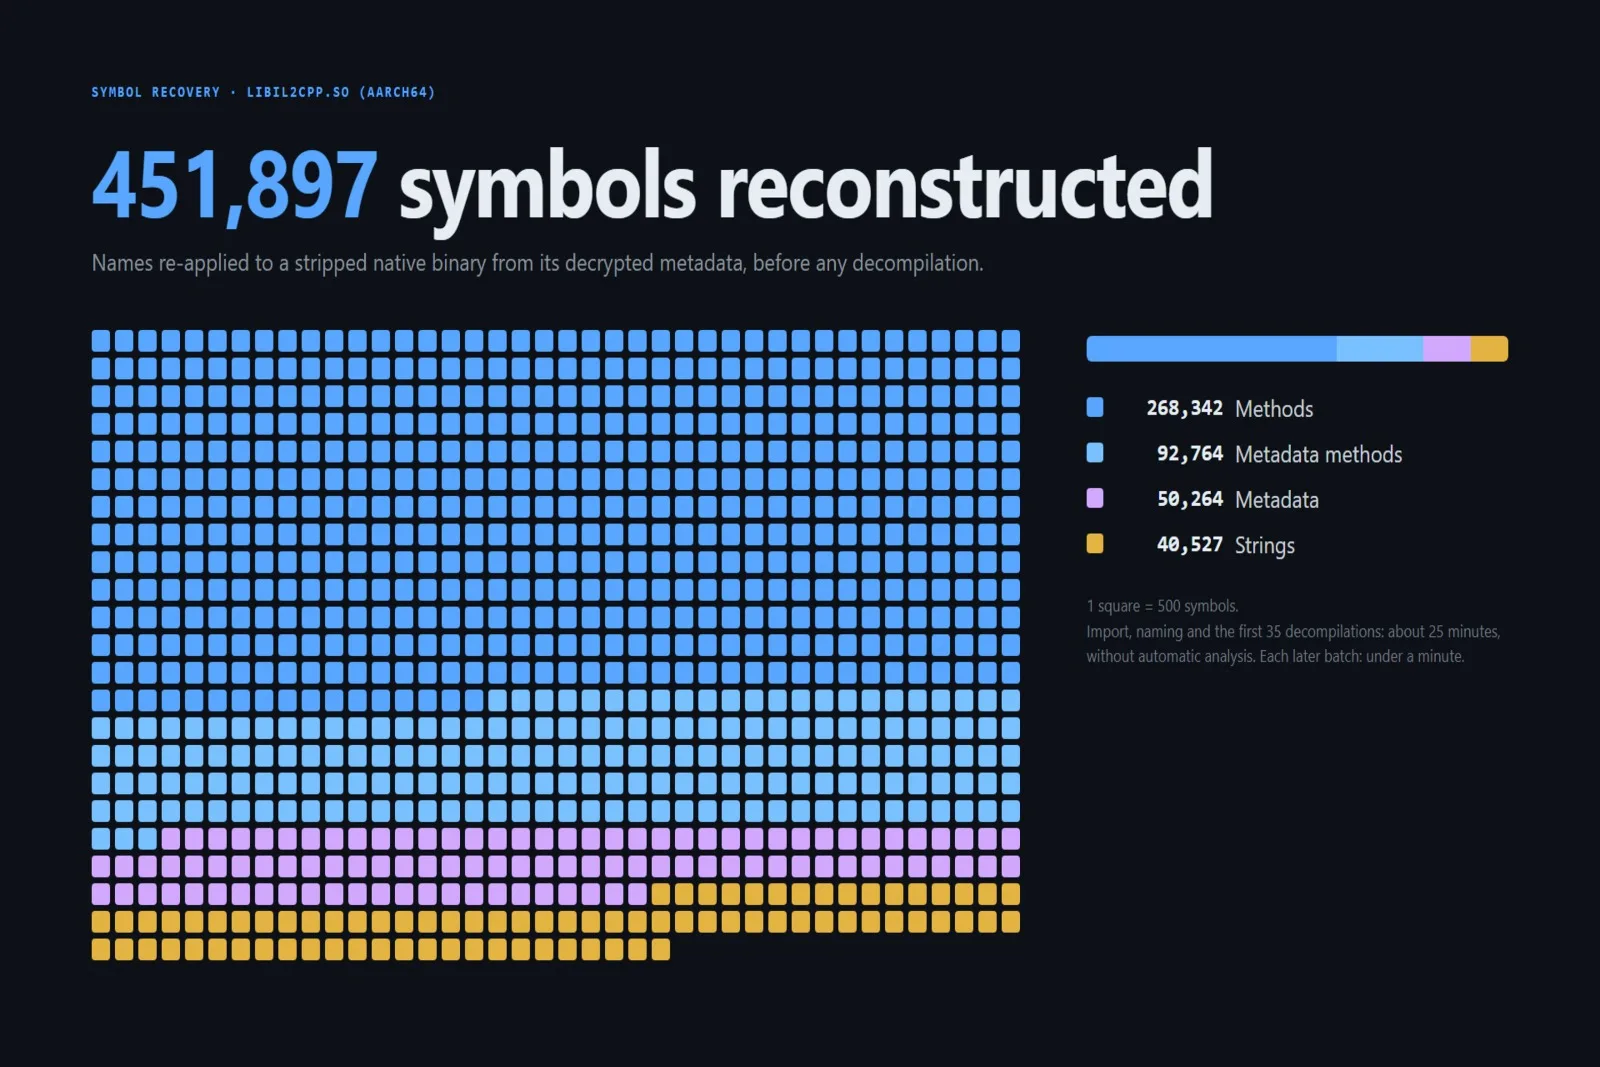
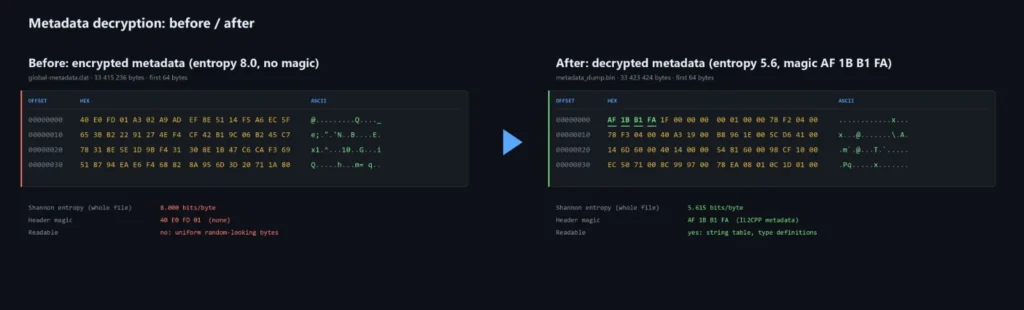
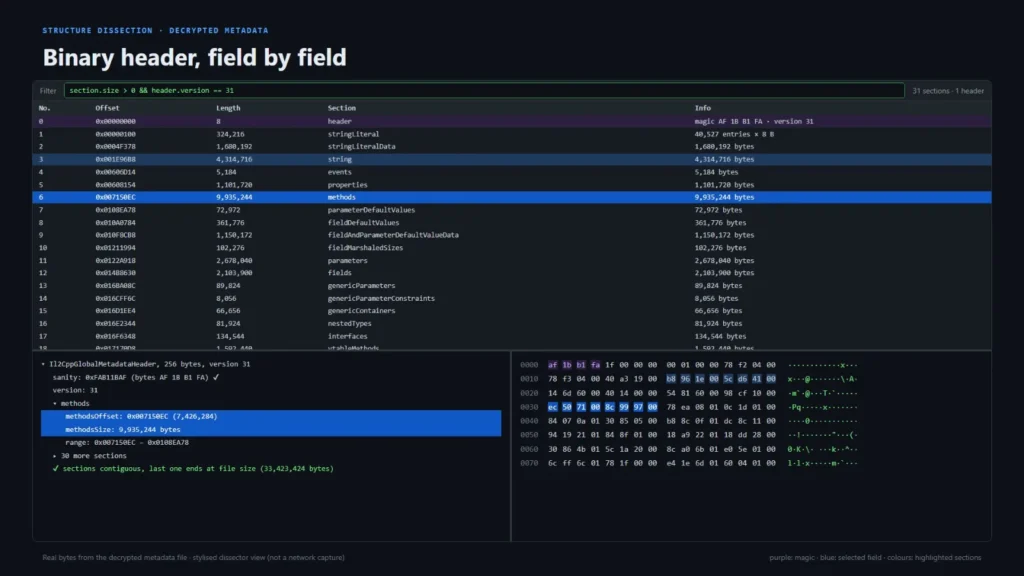
End-to-end reverse engineering of complex native binaries. From decrypting protected metadata (IL2CPP/Unity) to reconstructing full application logic, validated by over 800 automated tests. I turn stripped, unreadable binaries into clear, structured, and actionable intelligence.
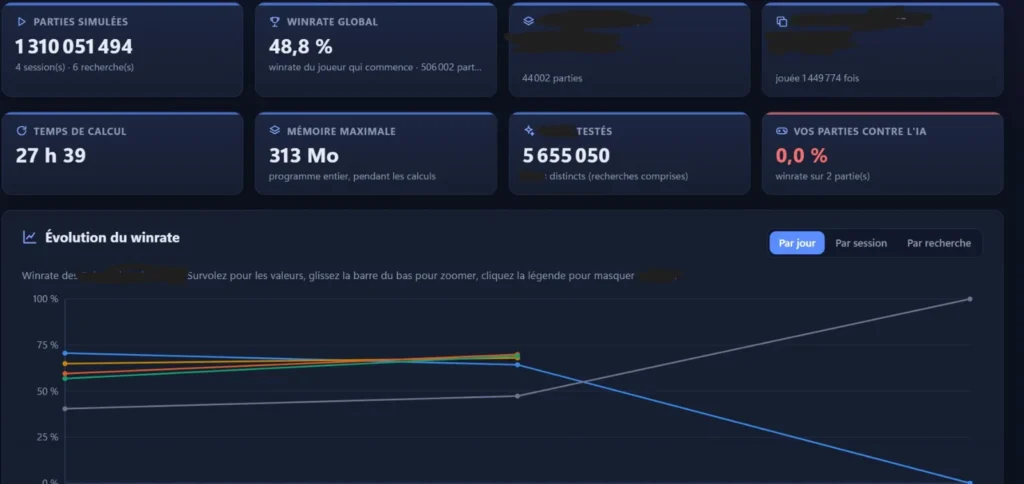
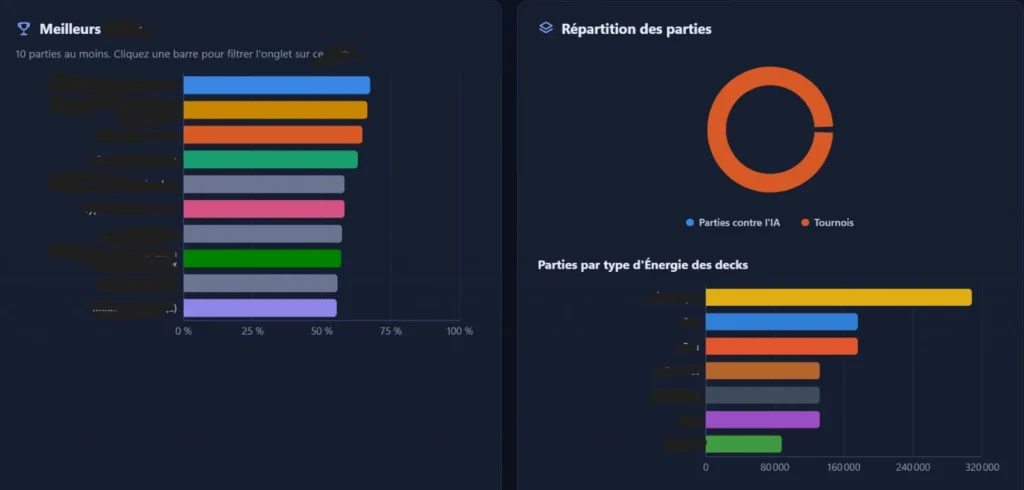
High-Performance Engine Development
Development of a high-performance simulation engine in Rust (capable of 600,000+ simulations per minute) with an advanced AI (MCTS) and a complete desktop interface (Tauri). Built to strictly replicate complex, extracted business logic with 100% fidelity
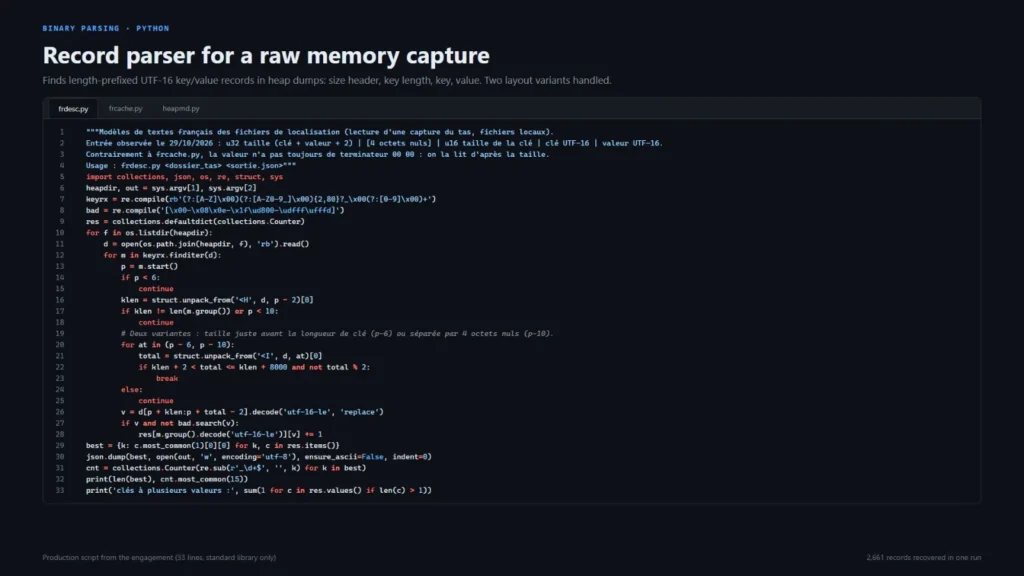
Data Extraction & Binary Parsing
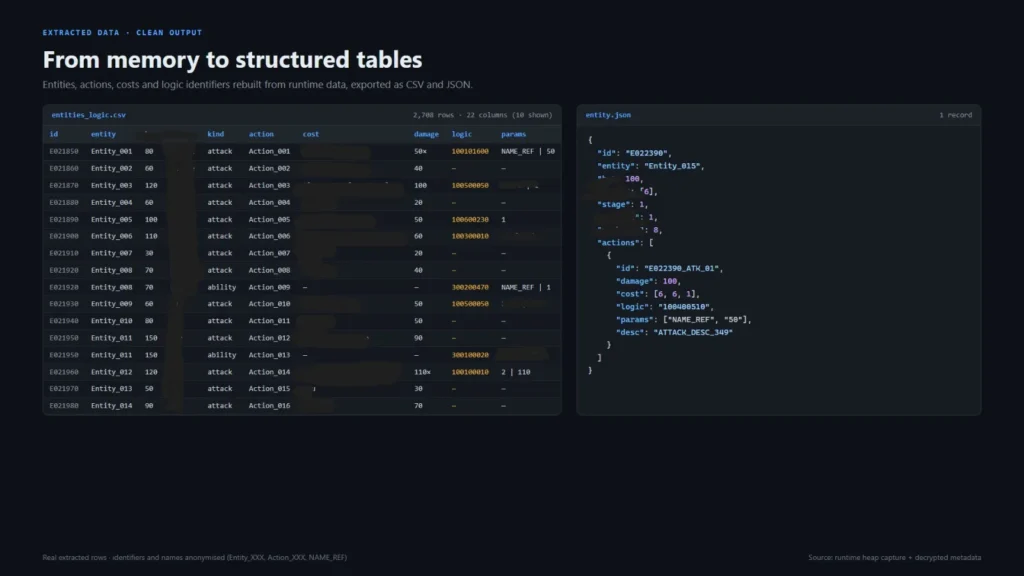
Custom tooling for extracting structured data from complex, encrypted or proprietary binaries. From raw memory captures and binary headers to clean, production-ready CSV and JSON outputs. I write robust Python parsers (standard library only) capable of processing thousands of records in a single run, turning unstructured files into actionable databases.
Extra Information
Tools & Tech Stack
Supported File Types
Service Details
Frequently Asked Questions
Absolutely not. Your binary is analyzed in an isolated sandbox environment, never connected to a live network. I never share your files, findings, or project details with third parties. All files are permanently deleted from my systems 7 days after delivery. I also sign NDAs (Non-Disclosure Agreements) upon request at no extra cost.
Yes. Unpacking and deobfuscation are part of my expertise. If the file is highly protected, it may require the Advanced package. However, I always review the file and confirm feasibility within 24 hours before we start.
I provide strictly written communication to ensure a detailed, traceable record of all findings. You will receive a comprehensive PDF report and 7 days of written Q&A support after delivery. This guarantees that you have everything documented in writing.
You will receive a clear, structured PDF report explaining the file's behavior, logic, and risks. Depending on your package, you may also receive extracted data (CSV/JSON), a list of Indicators of Compromise (IOCs), and Python scripts used for the analysis.
Customer Reviews
See what our customers say about this Zinn